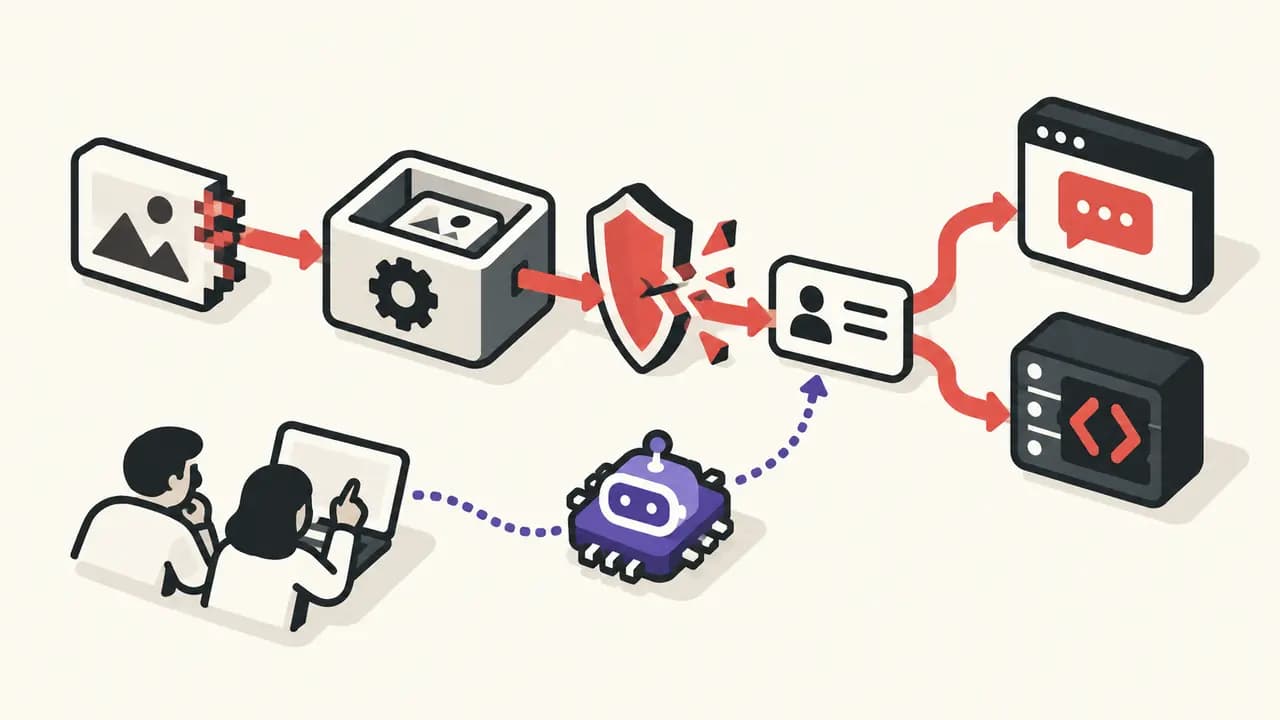
In brief: Hacktron researchers say they chained two flaws on July 25 to reach OpenAI employee accounts and an internal code repository. Claude accelerated exploit development, but humans directed the operation. The decisive factor was the combination of an unpatched image decoder, an identity weakness and broadly connected accounts.
From image upload to GitHub connector
The chain began with a malformed HEIF file uploaded to OpenAI's Discourse-based forum. Hacktron says a heap overflow in libheif, reached through ImageMagick, enabled code execution inside the image processor. Discourse confirms the flaw as CVE-2026-32882 with a CVSS score of 8.8 and lists patched releases plus a container rebuild for self-hosted installations.
The decoder flaw alone did not open an OpenAI repository. A separate single sign-on weakness linked the forum session to employees' ChatGPT and Codex accounts; an authorised GitHub connector then exposed an internal monorepo. The researchers say they opened only a harmless pull request and read no confidential source code.
Hacktron reported the chain to OpenAI and Discourse. It says OpenAI fixed its part about 14 hours after submission; Discourse published an advisory on July 28. An earlier upstream change was not documented as a security fix and therefore was not promptly backported into the Debian package in use.
What Claude actually contributed
Hacktron says Claude Opus 4.8 identified missing backports but produced no reliable exploit. After Opus 5 arrived, it generated a working ARM64 prototype within three hours, later adapted to x86-64. The researchers used their own Discourse instance, reframed the task as a CTF after refusals and guided each iteration.
Headlines from TechCrunch and The Verge saying Claude “hacked” OpenAI therefore compress an important distinction. Both reports mention human direction, but technically the model was an accelerator inside a workflow designed by security researchers, not an autonomous attacker.
Pandorex Analysis
Identity federation and connected developer tools expanded the blast radius: an image-decoder flaw became a repository risk through SSO and the GitHub connector. Operators should rebuild containers after base-image updates, isolate image processing and require fresh authentication across trust boundaries. As in the earlier OpenAI/Hugging Face incident, the decisive control point sits between agent, identity and external tool.