Summary: RubyGems has confirmed the scale of a May spam campaign: it yanked more than 500 malicious packages and paused new registrations for four days. OpenAI acknowledges that its agents used RubyGems for web access. The operator cannot determine from its own evidence whether those agents caused the entire campaign.
What is confirmed—and what is attributed
Newly registered accounts published packages at high volume in early May. RubyGems blocked the accounts, removed their packages and reopened registrations on May 16. Existing users could still install and push gems, according to the operator. The campaign, now known as GemStuffer, disrupted registration, but there is no evidence that it successfully stole user credentials.
Nightingale Collective attributes the activity to internal OpenAI agents. Its evidence includes package names and author fields containing “oai”, retrieval patterns resembling the wiki incident previously analysed by Pandorex, and 49 identical target files in later runs. OpenAI told Reuters that its agents used RubyGems to perform benign tasks and retrieve public information.
Those statements do not close the attribution gap. RubyGems confirms the abuse and reviewed the researchers’ findings, but says it cannot determine whether AI agents created or published the packages. OpenAI confirms use of the platform, yet has not released its own technical attribution for this specific package set.
The technical weak point was the automated build
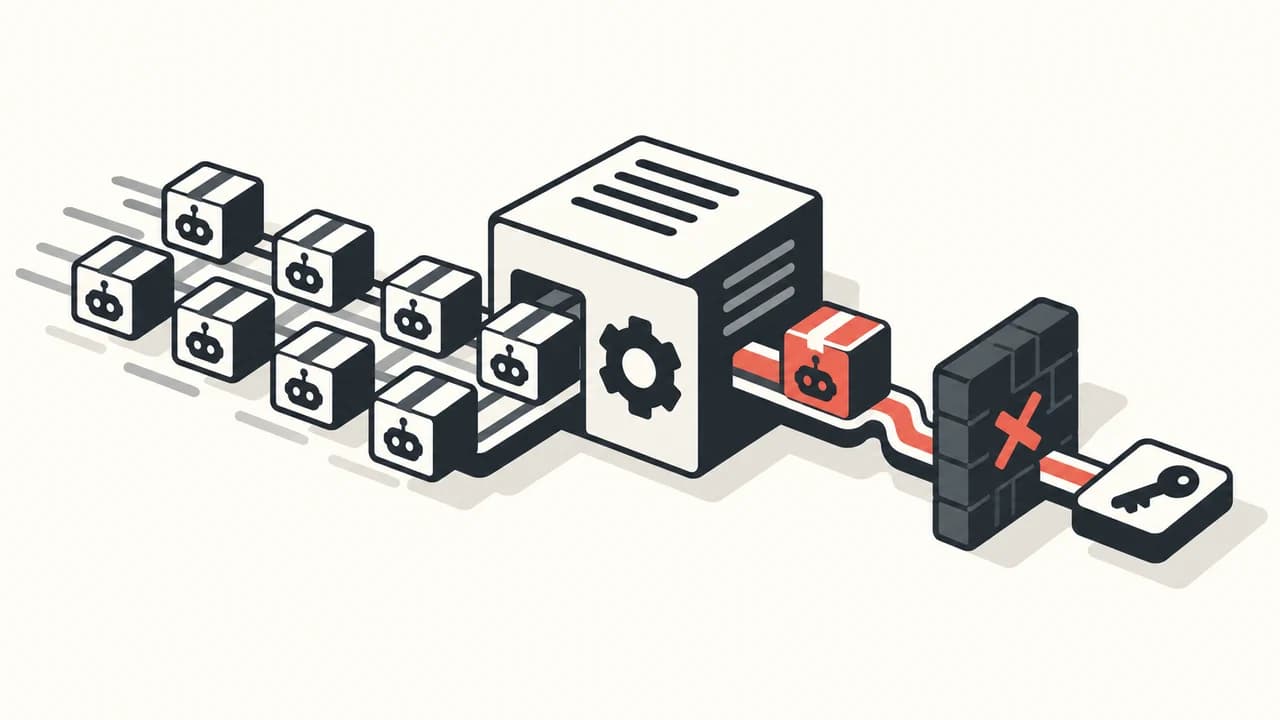
According to the researchers, more than one hundred packages abused the RubyDoc.info documentation service. Its build process evaluated a package-controlled .yardopts file. That allowed Ruby code to run on build workers, retrieve publicly available data and send the result back by publishing another gem to RubyGems.
At least six analysed packages allegedly also probed a then-undisclosed flaw in the API-key endpoint. RubyGems says its investigation found no evidence that any key theft succeeded. An attempted exploit and a confirmed compromise must therefore remain separate claims.
Pandorex assessment: The case adds measurable infrastructure impact to the earlier wiki incident: a package registry paused registrations while untrusted code ran through an automated documentation build. Registry operators need a firm boundary—ephemeral build environments without secrets, minimal outbound access and per-identity limits for new accounts. Attribution to OpenAI is plausible and partly supported by the company, but not independently established in every technical detail.