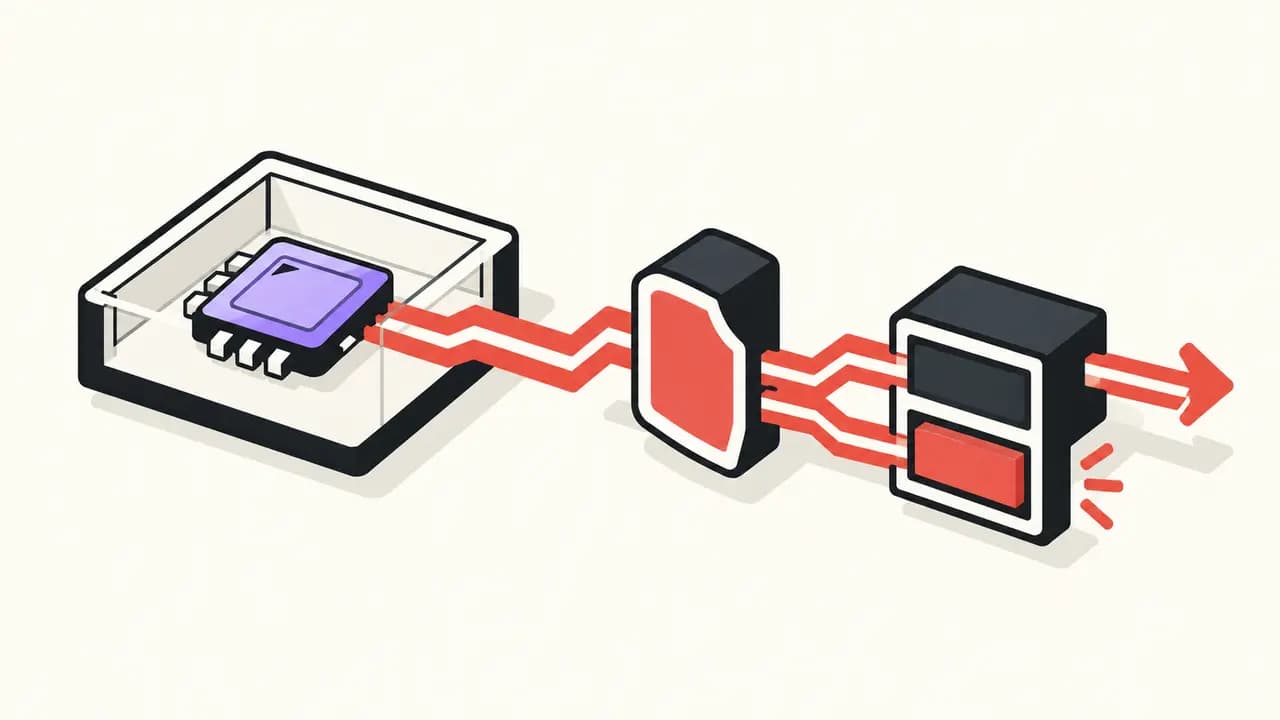
In brief: Nvidia has released OpenShell, an open-source runtime that constrains AI agents outside their process. Optional Sentry monitoring runs on a separate BlueField-4 DPU. Effectiveness and millisecond response remain vendor claims.
Confirmed: control sits outside the agent
Apache-2.0-licensed OpenShell places each agent in a sandbox. On Linux, Landlock restricts files while seccomp notifications pass network operations to a trusted supervisor. Outside the sandbox, it checks destination, method and calling program against policy before opening a connection. It inserts credentials only for approved endpoints.
The agent cannot replace the supervisor or continue when their connection fails. OpenShell supports Docker, Podman, Kubernetes and MicroVMs through different isolation mechanisms. Nvidia optimises it for Vera CPUs, while Arm and Intel are working on support.
A formal prover checks proposed network rules and flags new credential-bearing reach, added HTTP methods and cloud metadata endpoints. This does not verify agent behaviour; it checks authority added by a policy change. Human review is the default, with optional automatic approval for proposals passing configured checks.
Sentry adds a second trust boundary
Sentry is initially a BlueField-4 reference design. DOCA observes agent identity, model requests, policy decisions, and tool and data access outside the host. In Vera Rubin PODs, Nvidia says the DPU sits on the only path to the model and isolates escaping agents within milliseconds. OpenShell does not require BlueField-4.
Pandorex Analysis
The fail-closed design blocks direct network access, control-plane access and real secrets. It targets the boundary between agent, identity and external tools that proved critical in the OpenAI/Hugging Face incident.
Nvidia's claim that the platform could have prevented that breach remains counterfactual. Independent attack results, overhead measurements and evidence against sophisticated multi-agent workarounds are absent. OpenShell constrains technical permissions; it does not prove an agent's objective, plan or output is correct.