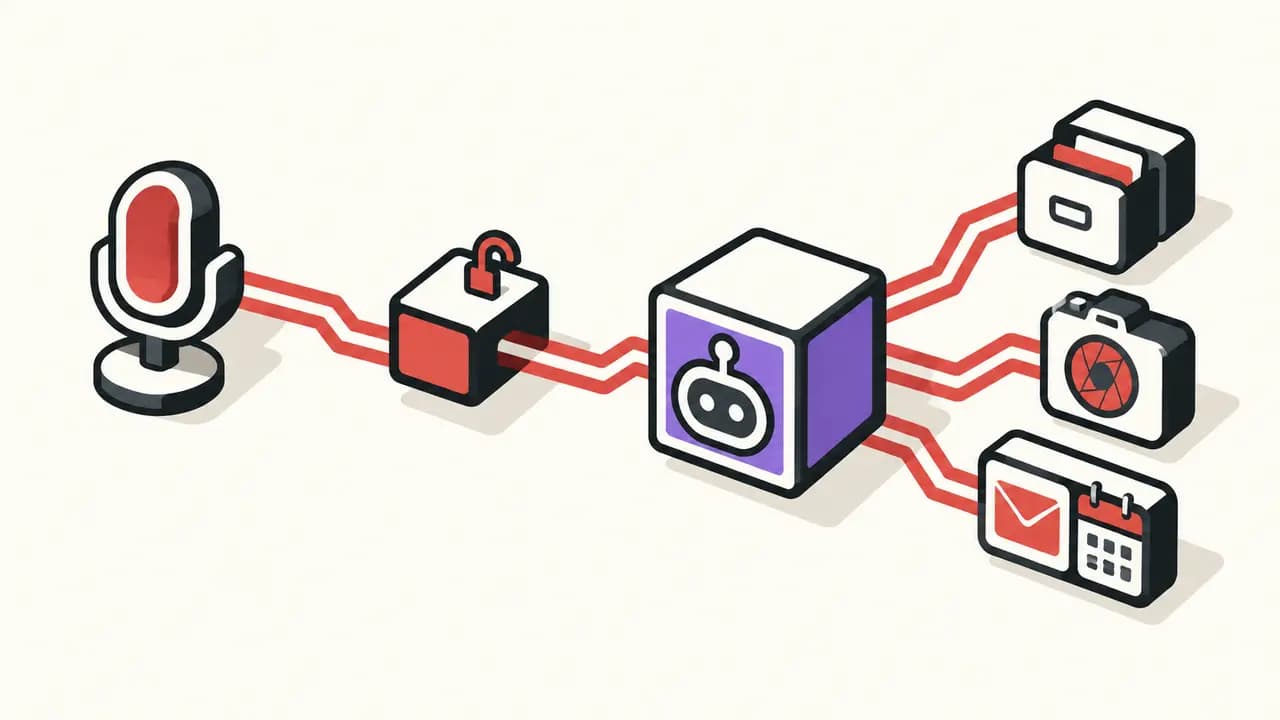
In brief: A local process could redirect Meta's Muse macOS agent to an attacker-controlled dictation endpoint through an unprotected setting. This enabled interception of input and command injection into an already authorised agent. Meta shipped a hotfix but published neither a CVE nor an identifiable fixed version.
Confirmed: local, but with broader reach
macOS security researcher Patrick Wardle found the undocumented endo_voyager_dictation_endpoint setting. Software running as the user could change it without special privileges, causing Muse to route dictated requests through a chosen server. Wardle's proof of concept demonstrates audio and prompt capture, injected instructions and access to authentication material.
This was not a remote entry point: malicious code first had to run under the affected account. The flaw could then amplify that foothold. Wardle's recreation implements part of more than 50 Muse commands. Access to files, messages, calendars, the camera or other data depends on permissions already granted to Muse. Reports of taking photos and writing files describe abuse of those permissions, not unauthenticated remote access.
Hotfix without a public version boundary
Meta executive David Singleton confirmed a hotfix on September 22 and called the issue a local privilege-escalation attack, matching the technical prerequisite. Meta has not published a security advisory listing a CVE, affected builds or a fixed version. Administrators therefore cannot use a documented version matrix to confirm remediation. Muse should be updated and successful installation of the app update verified.
Pandorex Analysis: delivery is not the vulnerability
Wardle notes that an attacker could deliver local code through ClickFix-style social engineering. That does not turn the Muse flaw into a remote exploit: deception supplies the initial local access, and Muse expands its effect. Meta's description of the prerequisite and Wardle's warning about the practical chain are therefore less contradictory than the debate suggests.
For enterprises, the difficult-to-observe delegation is the key issue. The final actions come from a signed agent operating with user-granted access. Until Meta identifies a verifiable fixed version, teams should allow Muse on managed Macs only after updating, investigate unusual Muse preference or dictation-endpoint changes, and minimise agent permissions. No evidence of active exploitation has been published.